Design the architecture before the infrastructure exists.
Model your system, add security context, then scan reachability, identity, vulnerabilities and attack paths before deployment.
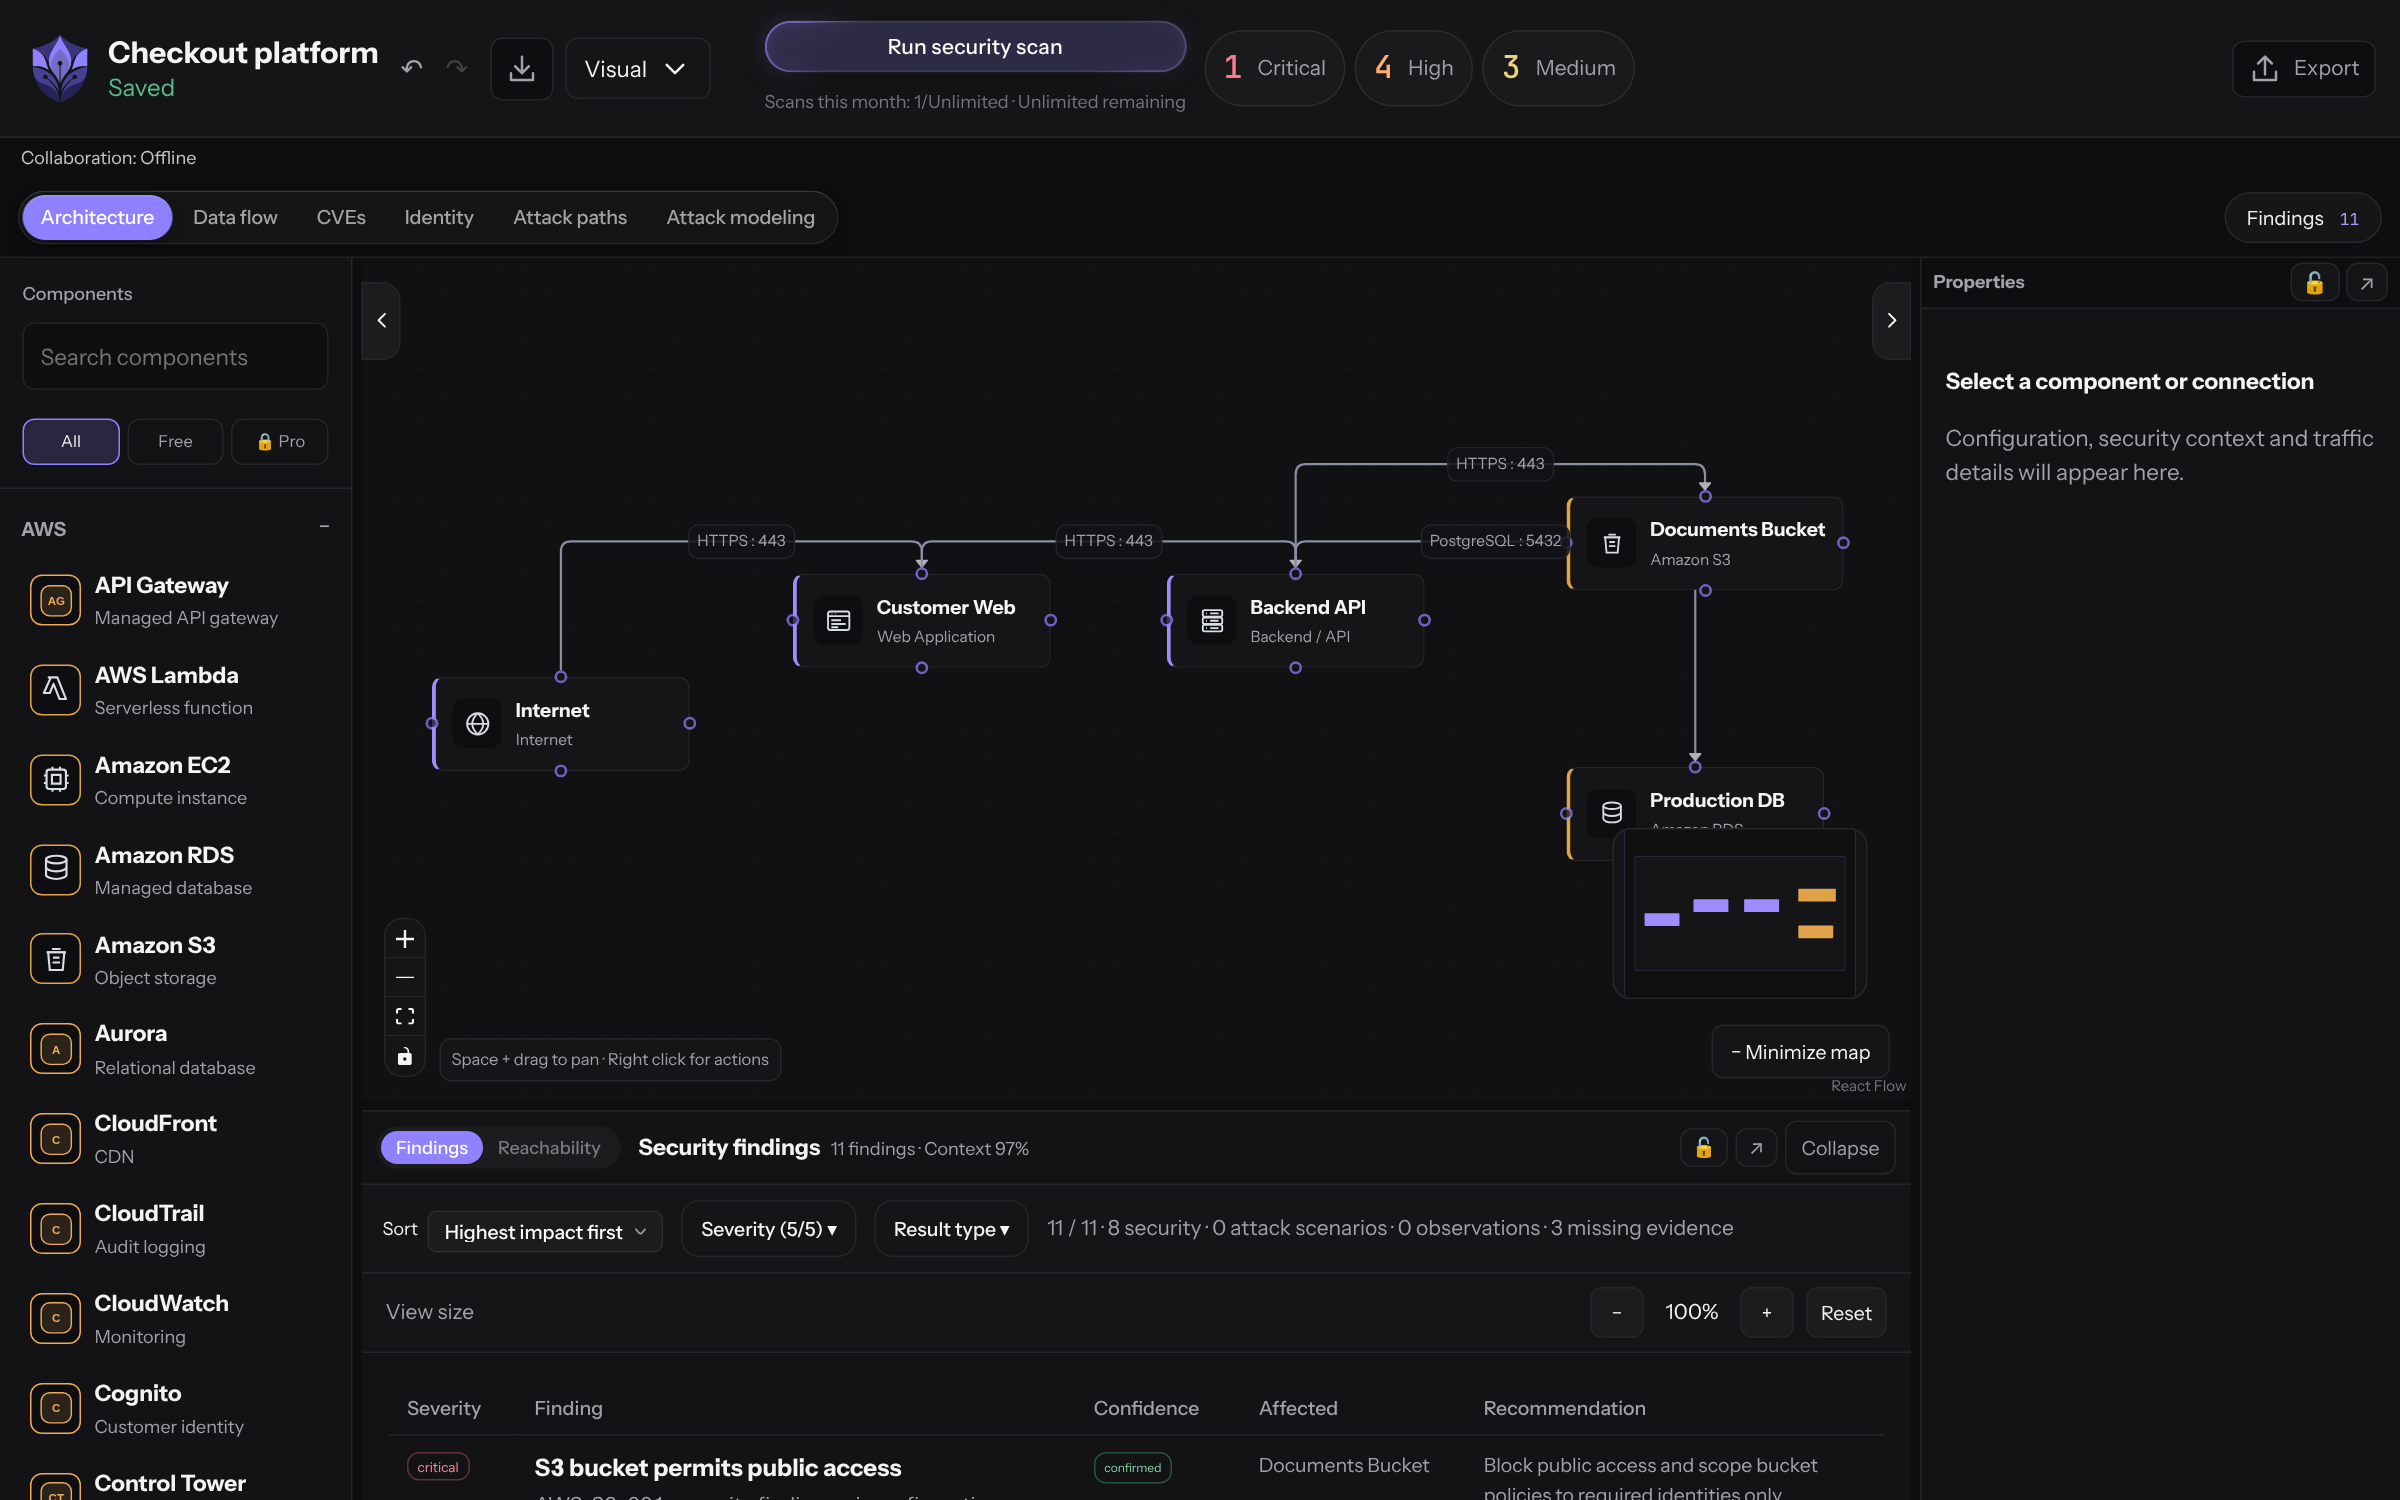
Model the system you actually intend to ship.
Drag infrastructure and application components onto the canvas, connect trust boundaries and flows, then add the context Shield needs to reason about risk.
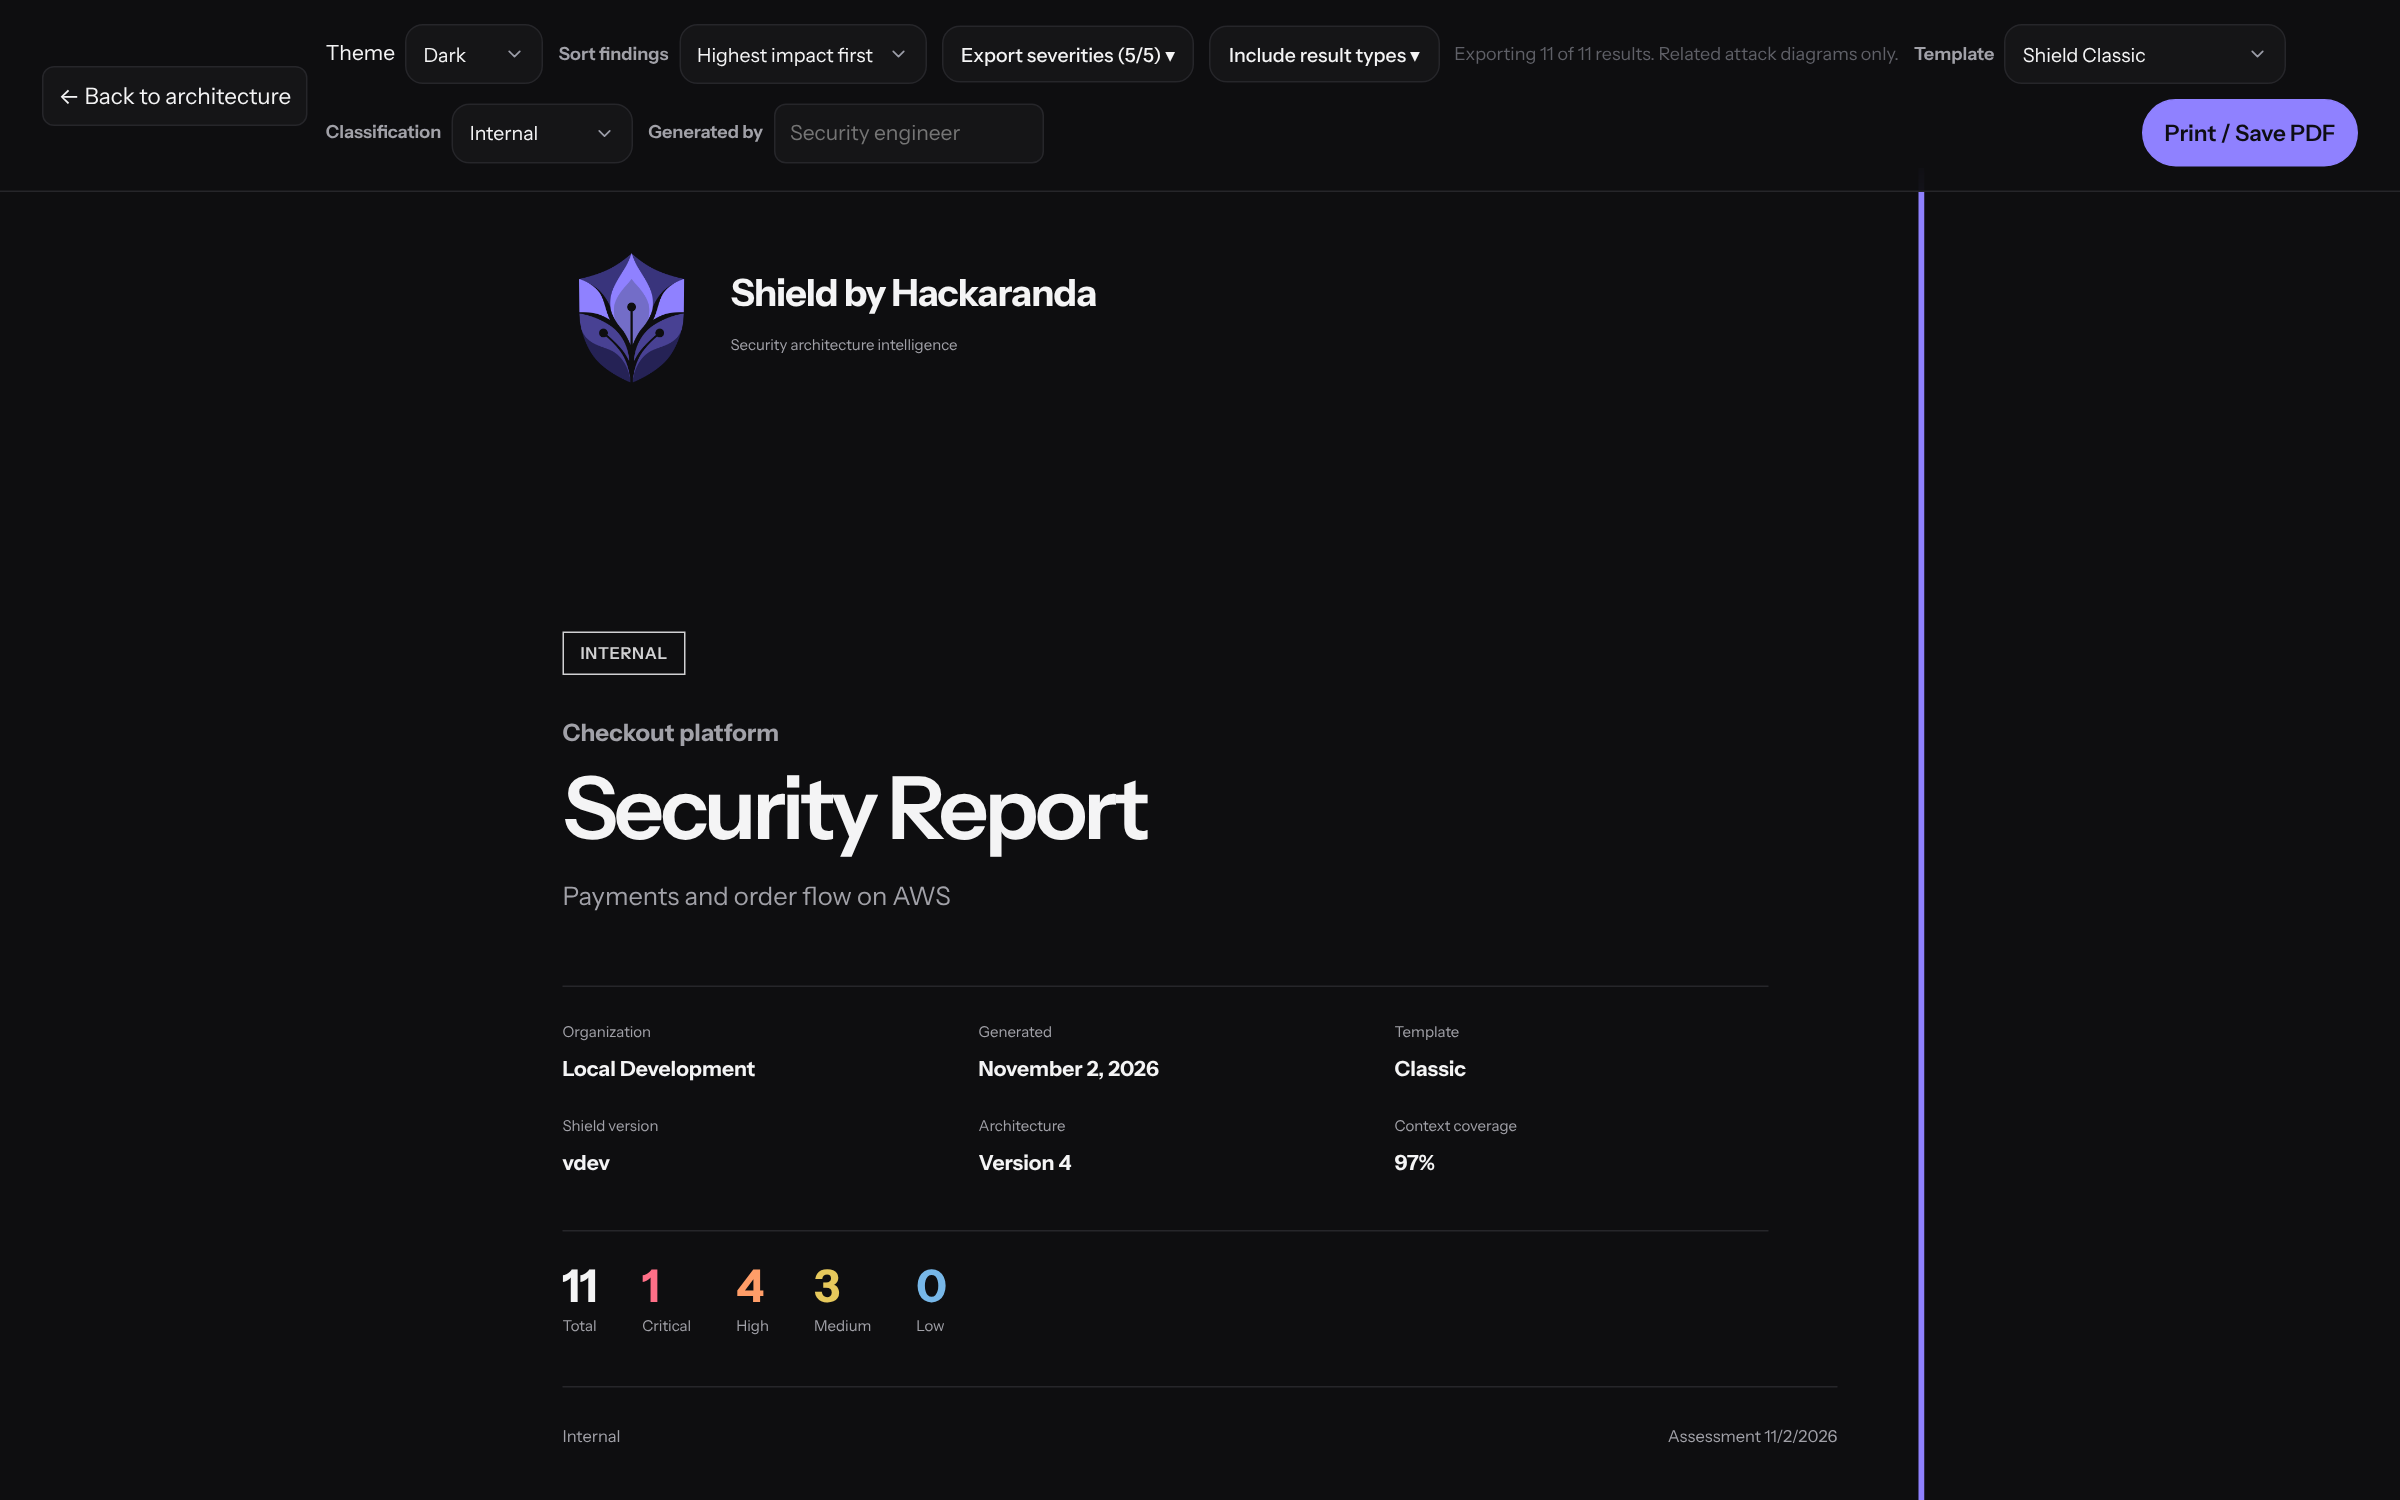
Turn architecture context into evidence your team can review.
Choose a template, set the data classification and export findings, attack paths, identity analysis and blast radius for technical and executive review.
Security starts before deployment.
Model components, network paths, trust zones, software inventory, sensitive data and business context while the architecture is still easy to change.
What can reach what, and who can become whom.
Correlate network reachability, IAM principals, permissions, bindings and trust relationships instead of reviewing those signals in isolation.
Plausible routes through the architecture.
Attack paths, attack trees and correlated blast radius, every result tied back to the architecture that produced it.